Find every credential. Stop the next breach.
Secure every credential across your entire secrets surface. From developer laptops and AI agents to code, public repositories, collaboration tools, and non-human identities.


Monitor
Every surface, always scanned

Detect
550+ detectors, live validity

Investigate
Context, owner, blast radius

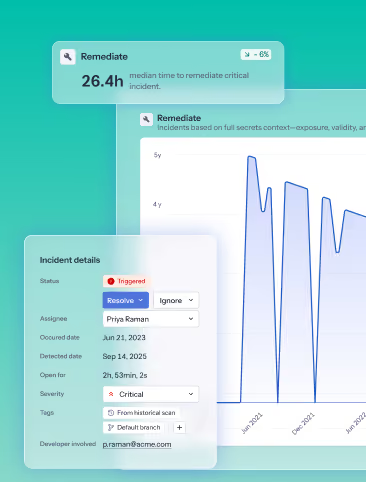
Remediate
Routed rotation playbooks

Prevent
IDE and AI tool guardrails

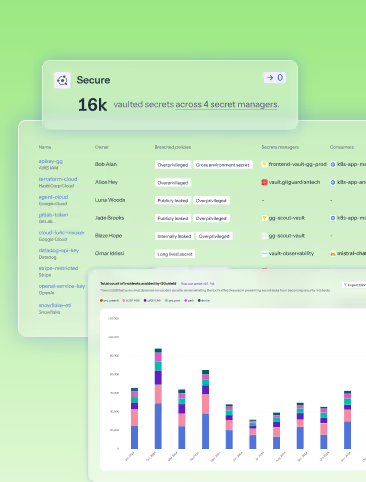
Secure
NHI inventory + governance



The outcomes teams actually report
15x
more valid secrets on endpoints than in repos
GitGuardian data analysis
97%
faster remediation
(from 37 days to 1 day)
European distribution leader
80,000+
occurrences prevented per month at commit time
A US telco leader
One platform.
Three connected pillars.
A leaked credential only stops being a breach path if you find it, resolve it, and prevent the next one. Existing tools cover one pillar each. GitGuardian is the only platform that does all three, for every credential across every surface your team owns.
Find every credential, everywhere it lives.

Monitor
Continuous coverage across code, CI/CD, containers, developer endpoints, cloud IAM, vaults, AI coding tools, and collaboration platforms. Public GitHub monitoring extends to personal-repo perimeter, where 80% of corporate credential leaks originate.

Detect
550+ detectors with live validity checks against the issuing provider. Contextual analysis suppresses test fixtures and dead keys, so your queue holds exploitable credentials, not regex matches. Historical scan replays years of git history on connection.
Route every incident to the right owner. Close it at scale.

Investigate
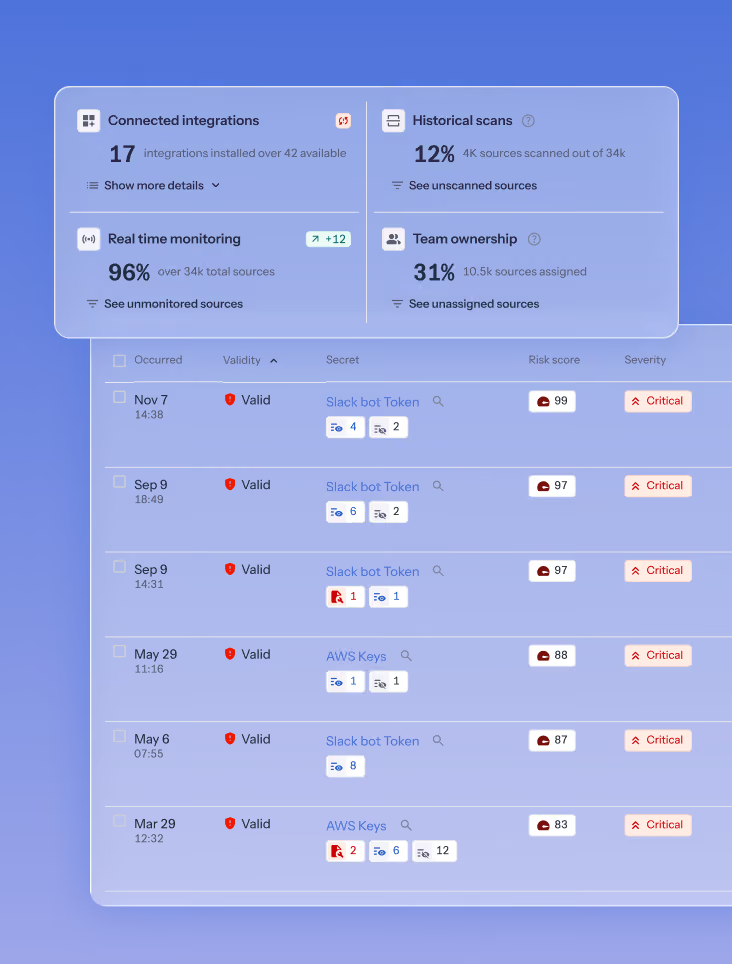
Automated severity scoring based on validity, exposure surface, and blast radius. AI-powered risk scoring and filters prioritize what actually matters. Saved views and occurrence grouping keep the queue navigable at enterprise scale.

Remediate
Auto-assigned incidents with per-detector rotation playbooks. Native integrations with Slack, Teams, Jira, and ServiceNow. Webhooks feed your SIEM, SOAR, and ITSM. AI false-positive removal keeps analyst time on real threats.
Stop new leaks. Govern every non-human identity.

Prevent
Developer-side guardrails at every stage. ggshield CLI with pre-commit hooks, VS Code extension, and AI IDE hooks for Cursor, Claude Code, Codex, and GitHub Copilot. Pre-receive hooks block risky pushes. Included with every plan.

Secure
Discover and inventory every non-human identity across vaults and cloud IAM. Map ownership, surface duplicated and reused secrets, and monitor OWASP Top 10 NHI coverage. Push detected secrets into your vaults for safe rotation.
Together, these capabilities close the loop from leak to identity, and back.
Every surface where credentials live.
Covered from one platform.

Covered from one platform

Container and package registries
Images and published packages


Cloud IAM
AWS, GCP, Azure


Vaults
HashiCorp, AWS Secrets Manager, Azure Key Vault


Developers Endpoint
HashiCorp, AWS Secrets Manager, Azure Key Vault


AI coding tools
Cursor, Claude Code, Codex, Copilot


Collaboration platforms
Jira, ServiceNow, Slack, Confluence — Enterprise


Public GitHub
The personal-repo perimeter


Source code
GitHub, GitLab, Bitbucket, Azure DevOps


CI/CD pipelines
Build logs, runners, job artifacts


Fifty-plus integrations. VCS-agnostic by design.
Built for the teams that own credential
security together.

Reduce the risk of credential breaches with metrics your board understands.
- Report mean time to detect in seconds and mean time to remediate in hours, not weeks
- Consolidate the secrets program: one platform, one queue, one contract
- Ship SOC 2, ISO 27001, and PCI DSS evidence without spreadsheet assembly before every audit


"GitGuardian lets us analyze the entire GitHub perimeter including developers' personal repos outside our control."
CISO, Qlik

Validity-checked incidents, workflow-native remediation, no false-positive fatigue.
- Every alert is a validated, exploitable credential, not a regex hit
- Rotation playbooks per credential type with SLA tracking and role-based access
- Native webhooks push signal into your SIEM, SOAR, and ITSM stack
"When we decided to block new secrets in the repository, the amount of secrets dropped by 60%. So that's the main ROI of using GitGuardian."
Olivier Ribardiere, Head of CI/CD & Frameworks, Bouygues
Security that meets you where you already work.
- ggshield CLI, pre-commit hooks, VS Code extension, AI IDE hooks, included on every plan
- Cursor, Claude Code, Codex, and GitHub Copilot integrations catch credentials before they reach the model
- Sub-second incremental scans, no CI latency
"Our security productivity has increased significantly. Simply by making this information readily available to developers, we've empowered them to take action."
Joan Ging, Head of Development, Inhabit
Explore what's inside the platform
Find, fix, and prevent hardcoded secrets across code, CI/CD, and collaboration tools.

Catch corporate credentials leaked on public GitHub, including the personal-repo perimeter.
Scan credentials on developer machines, in AI agent caches, and across the local surface.
Inventory, map, and monitor every non-human identity across your vaults and cloud IAM.

See your credential attack surface before an attacker does.
Ready to go deeper? Talk with our team about your credential risks, security stack, and deployment needs.